
Compliance
NY DFS Part 500
Cybersecurity oversight extended to AI systems, with incident evidence and access records examiners expect.
At a glance
Who this covers, and who enforces it
Entities regulated by the New York Department of Financial Services, including AI systems that touch covered nonpublic information or covered business processes.
- Instrument
- 23 NYCRR Part 500 — state regulation
- Enforced by
- New York Department of Financial Services
- Timeline
- Effective 2017; second amendment Nov 2023
- Incident notice
- 72 hours
- Annual duty
- Compliance certification by a senior officer
Requirements
What it asks for
- 1Risk assessment that covers AI use
- 2Access controls and continuous monitoring
- 3Incident response with 72-hour notification
- 4Annual certification of compliance
Evidence mapping
What PRISM records against each requirement
Every plan records this evidence as your AI runs. Compliance Reports, which turn it into a reviewed, framework-mapped report, are delivered as a service, on request.
- AI-aware risk assessment
- Model Inventory and Synthetic Scenarios document AI-specific risk testing.
- Access controls & monitoring
- Guardrails and Projects & Team enforce and log access boundaries.
- Incident response
- Scores & Alerts flag anomalies in real time, feeding the 72-hour notification clock.
- Annual certification
- Export & Audit produces the evidence package a certifying officer reviews.
Primary source
Read the actual text
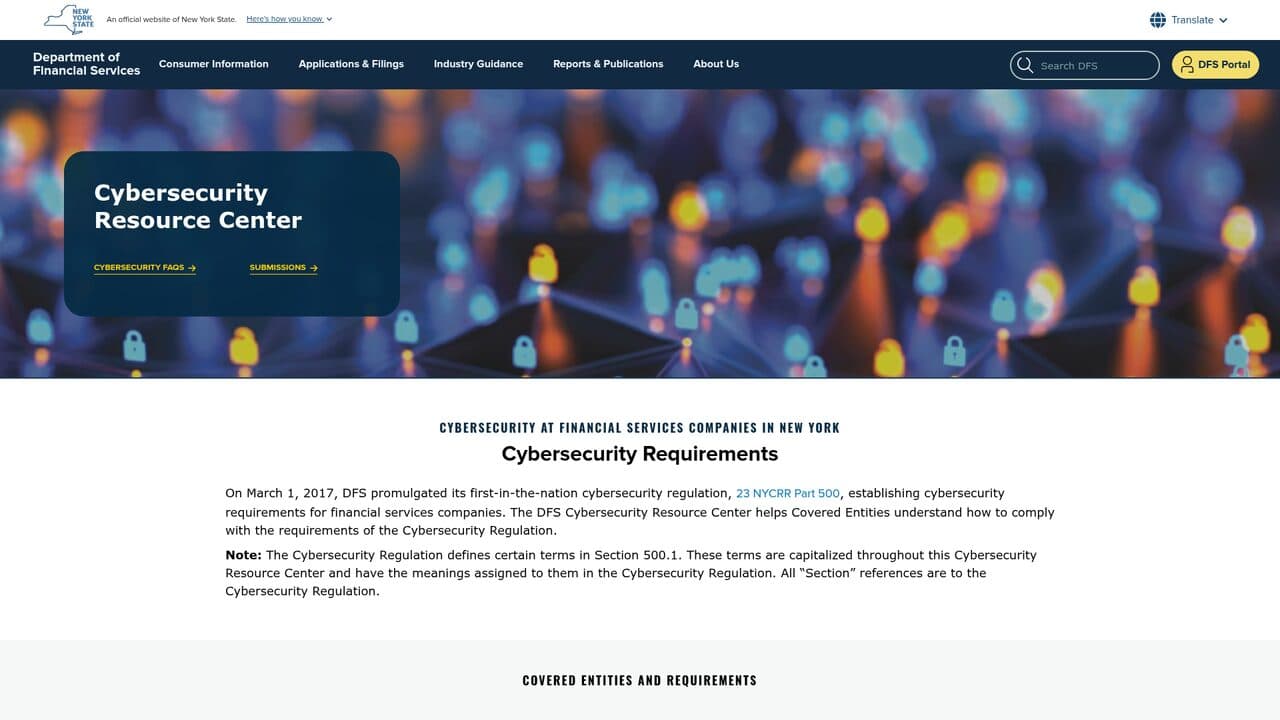
Everything on this page is drawn from New York DFS — Cybersecurity Resource Center (23 NYCRR Part 500). The capture is live, not a paraphrase — go straight to the source and check us.
Evidence, not certification
This page describes NY DFS Part 500’s publicly available requirements and how PRISM’s evidence layer supports them. It is not legal advice, and it does not constitute certification, regulatory approval, or a guarantee of compliance. NY DFS Part 500 compliance remains your organization’s responsibility, in consultation with qualified counsel.
Keep reading
- All frameworksThe full evidence-layer overview and all twelve frameworks.
- NAIC Model BulletinAI governance for insurers: documented testing, decision oversight, and incident handling with evidence attached.
- CFPB and Reg BAdverse decisions need explanations. Session-level evidence of what the model saw, did, and decided.
Ask us about your framework
Tell us how NY DFS Part 500 applies to your systems and we'll show you the evidence path.