
Compliance
PCI DSS
Cardholder data kept out of AI logs. Guardrail events and redaction evidence on the paths that matter.
At a glance
Who this covers, and who enforces it
Any organization whose AI systems store, process, or transmit cardholder data, including AI features layered on payment flows.
- Instrument
- PCI DSS v4.x — contractual standard
- Issued by
- PCI Security Standards Council
- Timeline
- v4.0 mandatory since 31 Mar 2024
- Enforced by
- Card networks and acquiring banks
- Exposure
- Fines, higher fees, loss of card acceptance
Requirements
What it asks for
- 1Cardholder data kept out of logs and prompts
- 2Access control and monitoring
- 3Regular testing of security systems
- 4Incident response procedures
Evidence mapping
What PRISM records against each requirement
Every plan records this evidence as your AI runs. Compliance Reports, which turn it into a reviewed, framework-mapped report, are delivered as a service, on request.
- Data kept out of logs
- Guardrails redact cardholder-data patterns before they reach a trace.
- Access control
- Projects & Team restrict who can view traces on payment-adjacent systems.
- Security testing
- Synthetic Scenarios probe for cardholder-data leakage before release.
- Incident response
- Scores & Alerts flag a redaction failure the moment it happens.
Primary source
Read the actual text
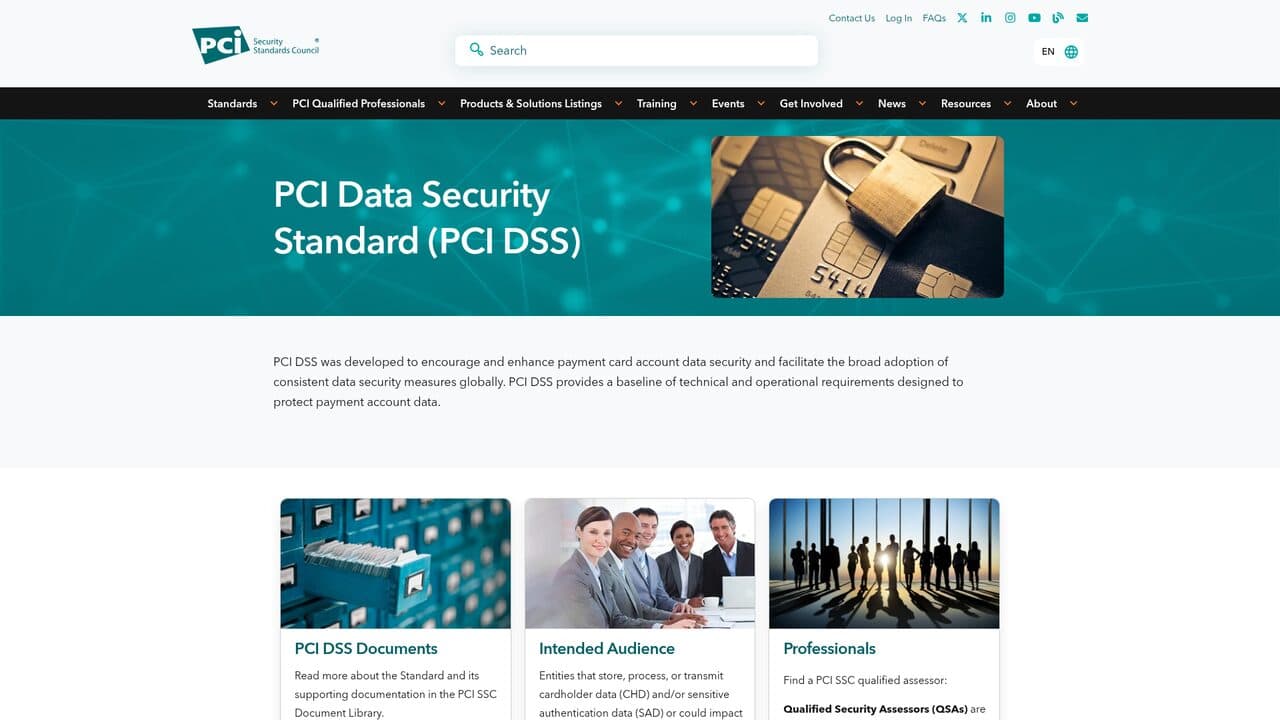
Everything on this page is drawn from PCI Security Standards Council — PCI DSS. The capture is live, not a paraphrase — go straight to the source and check us.
Evidence, not certification
This page describes PCI DSS’s publicly available requirements and how PRISM’s evidence layer supports them. It is not legal advice, and it does not constitute certification, regulatory approval, or a guarantee of compliance. PCI DSS compliance remains your organization’s responsibility, in consultation with qualified counsel.
Keep reading
- All frameworksThe full evidence-layer overview and all twelve frameworks.
- EU AI ActRisk classification, logging, and human oversight duties for AI systems in the EU. PRISM evidence shows what the system did and who approved each change.
- NIST AI RMFThe govern, map, measure, manage cycle. Traces, evaluations, and reviews become the measure and manage record.
Ask us about your framework
Tell us how PCI DSS applies to your systems and we'll show you the evidence path.